Systematic Analysis of Critical Factors for Value Management in Cybersecurity
Keywords:
value management, cybersecurity, critical success factors, telecommunications, cyber securityAbstract
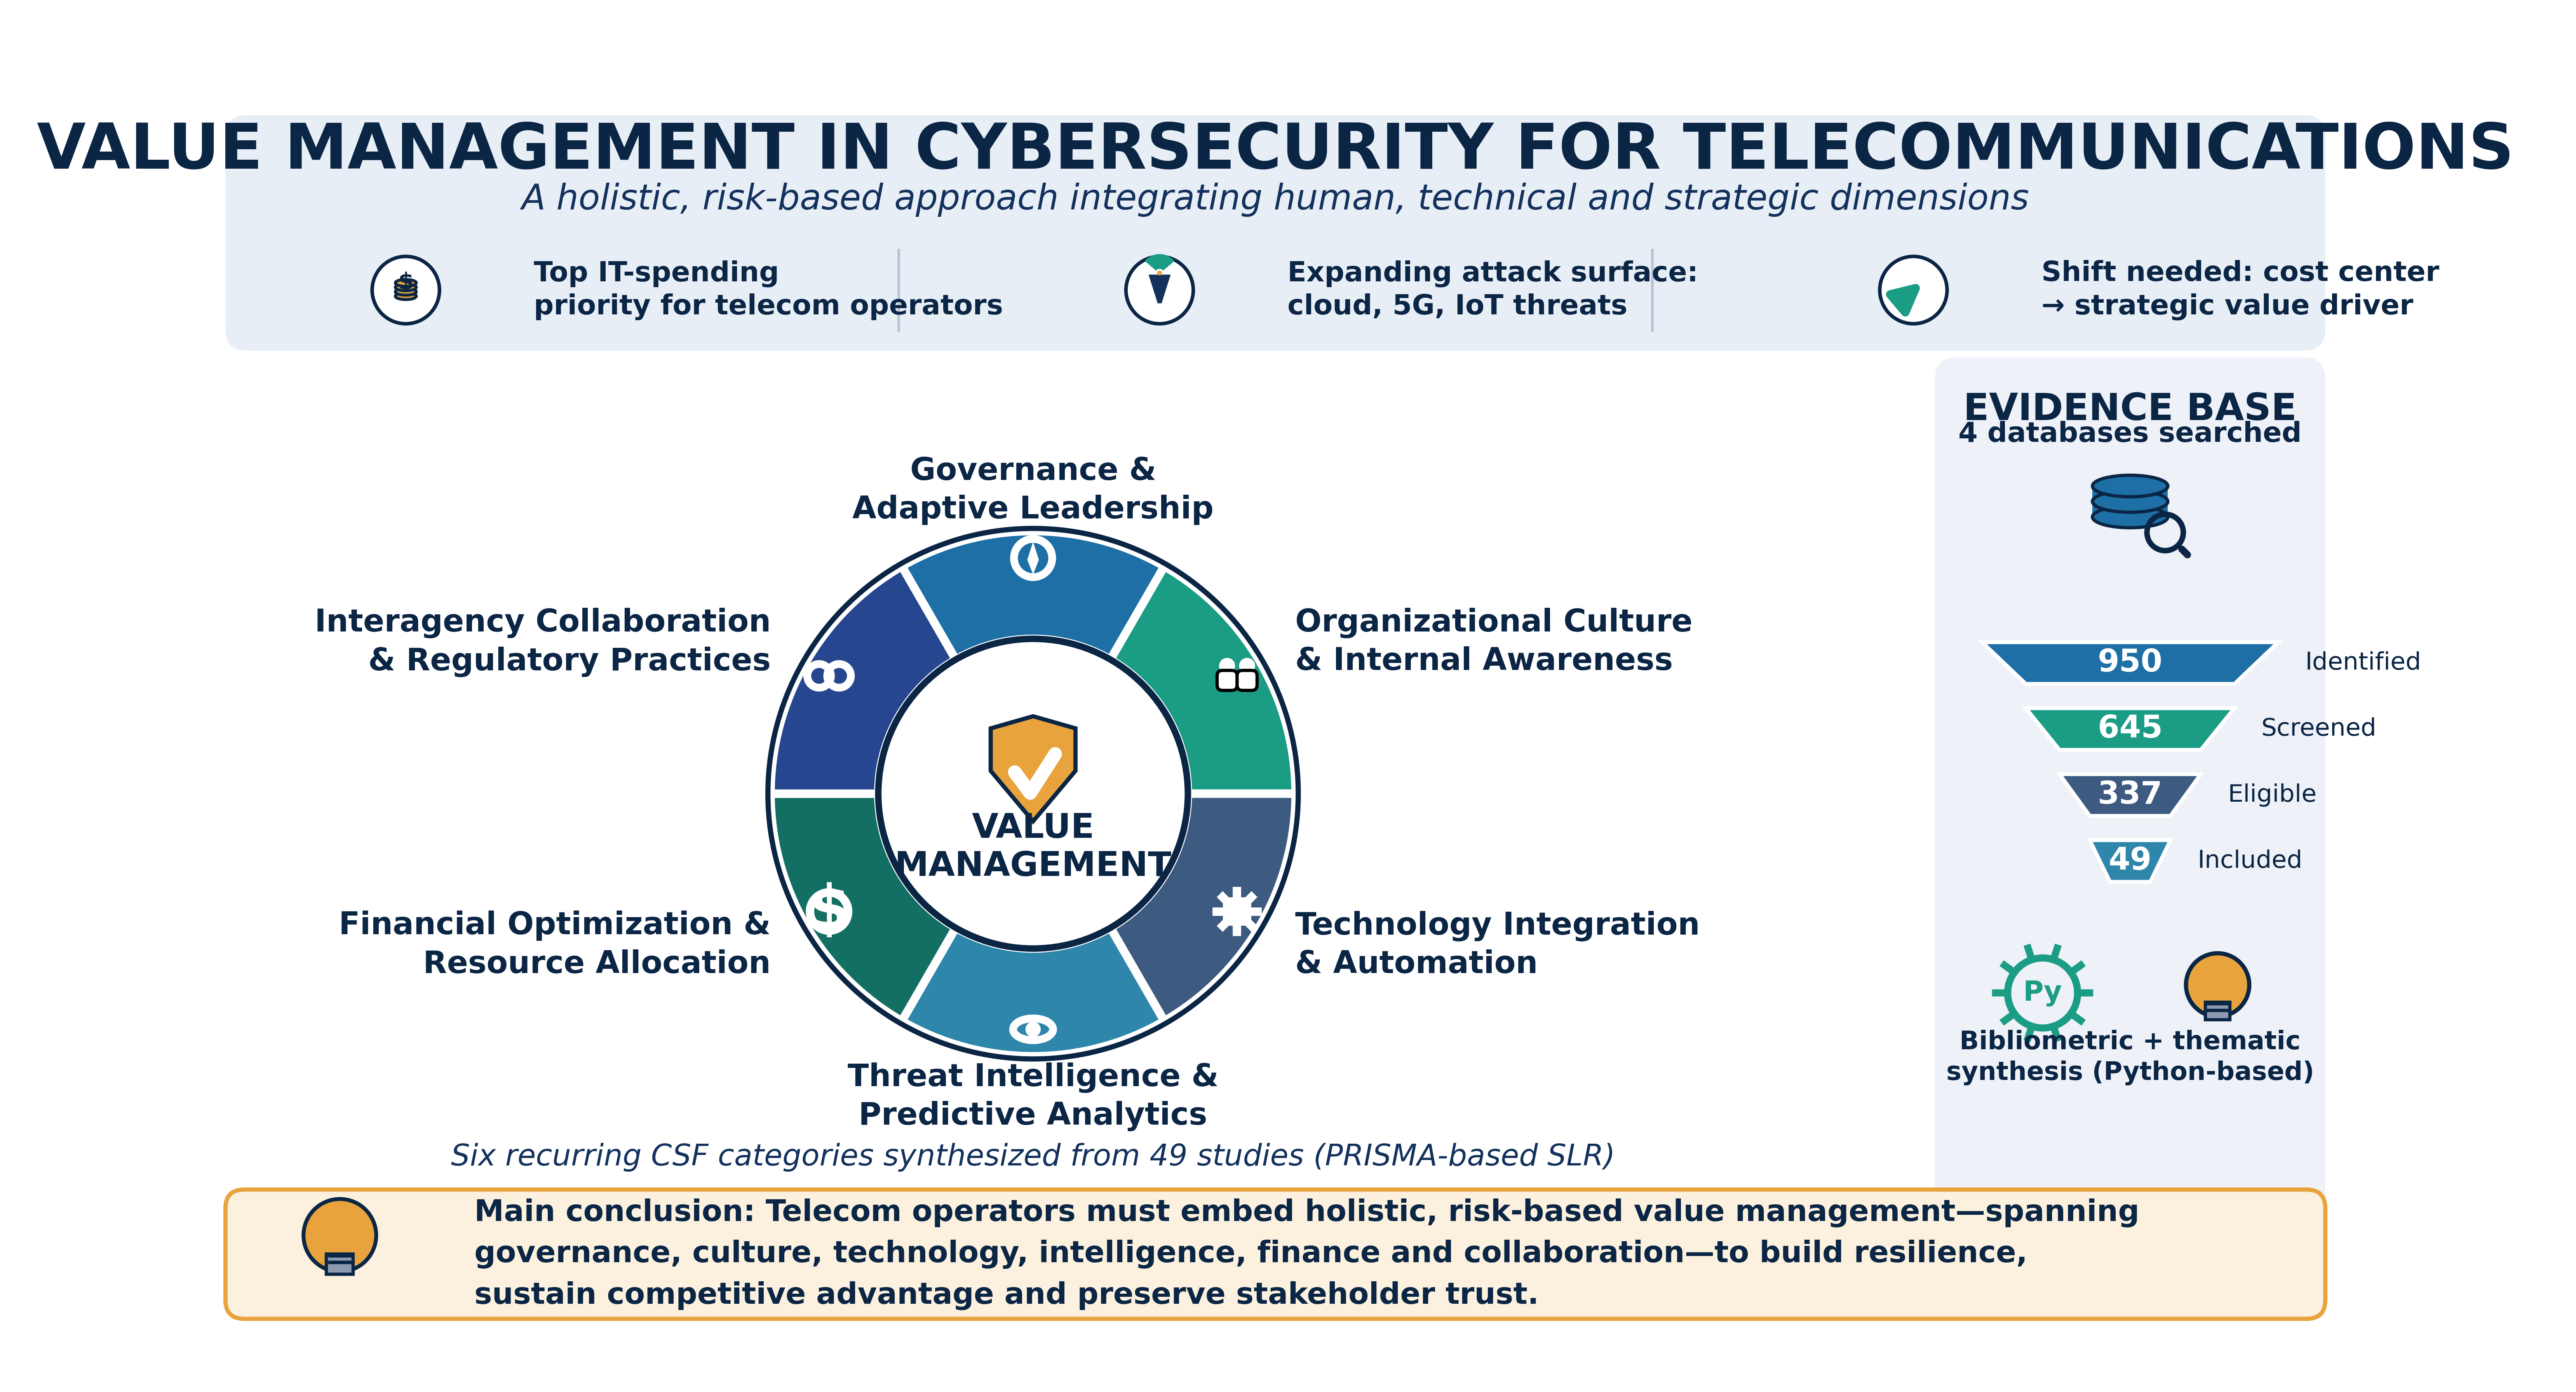
Existing studies indicate that cybersecurity ranks among the top priorities for IT spending in telecommunications organizations, and that value management is critical for defining effective cybersecurity policies and strategies that enable efficient resource allocation. This study aims to analyze and synthesize existing research on the critical factors underpinning the strategic relevance of value management in the cybersecurity of telecommunications organizations. A systematic literature review (SLR) following the PRISMA methodology was conducted across three phases: planning, execution, and reporting. The Consensus tool was used to search the Semantic Scholar, IEEE Digital Library, Scopus, and ScienceDirect databases, yielding 950 articles. After rigorous screening and eligibility assessment, 49 key articles were selected for qualitative synthesis. Python-based tools were used for bibliometric analysis. Results show that 2023 recorded the highest publication output, with the journal Sustainability leading in article distribution. Inter-institutional collaboration and organizational culture emerged as the themes generating the greatest research interest. Six recurring categories were identified, consolidating the critical success factors (CSF) of value management in cybersecurity within telecommunications companies. The findings suggest that effective cybersecurity value management requires a holistic, risk-based approach that integrates human, technical, and strategic dimensions. Organizations must prioritize continuous adaptation and resilience against evolving threats by leveraging collaborative ecosystems and information-sharing mechanisms. Furthermore, embedding cybersecurity within broader business, innovation, and value-creation agendas is essential for sustaining competitive advantage and stakeholder trust. Compliance with standards and the application of economic models for risk quantification ensure regulatory alignment and long-term financial sustainability.
Downloads
References
Netskope, “Cloud and Threat Report: 2025,” Netskope. Accessed: Sep. 28, 2025. [Online]. Available: https://www.netskope.com/resources/reports-guides/cloud-and-threat-report-2025
P. Barrios, “Telecom Cybersecurity Strategies That Protect Customer Information,” Valor Global. Accessed: Aug. 20, 2025. [Online]. Available: https://valorglobal.com/telecom-cybersecurity-strategies-that-protect-customer-information/
R. Watson and R. Bergman, “Cybersecurity: From value protection to value creation | EY - Global,” Cybersecurity: From value protection to value creation | EY - Global. Accessed: Aug. 20, 2025. [Online]. Available: https://www.ey.com/en_gl/insights/consulting/how-can-cybersecurity-go-beyond-value-protection-to-value-creation
Chitopoulos, “Amid Cyberthreats, Telecom Companies Must Balance Security with Innovation,” Cyber Defense Magazine. Accessed: Feb. 25, 2026. [Online]. Available: https://www.cyberdefensemagazine.com/amid-cyberthreats-telecom-companies-must-balance-security-with-innovation/
I. Balodis, “Cybersecurity in the Digital Age: Threats, Challenges, and Strategic Responses,” Feb. 19, 2025. doi: 10.2139/ssrn.5144431.
S. Garai and Z. Taskeen, “Emerging Trends in Cybersecurity: A Holistic View on Current Threats, Assessing Solutions, and Pioneering New Frontiers,” Blockchain in Healthcare Today, vol. 7, no. 1, 2024, doi: 10.30953/bhty.v7.302.
K. Jaggi, “Advancing Cybersecurity Strategies: Balancing Threat Detection, Compliance, and Resilient Architectures,” Feb. 04, 2025. doi: 10.2139/ssrn.5124287.
K. Khadka, “Forecasting Risks, Challenges, and Innovations: A Cybersecurity Perspective,” Dec. 21, 2024, Social Science Research Network, Rochester, NY: 5187659. doi: 10.2139/ssrn.5187659.
S. AlDaajeh and S. Alrabaee, “Strategic cybersecurity,” Computers & Security, vol. 141, p. 103845, Jun. 2024, doi: 10.1016/j.cose.2024.103845.
F. Heiding, A. O’Neill, and L. Price, “Cybersecurity Strategy Scorecard | The Belfer Center for Science and International Affairs.” Mar. 27, 2025. Accessed: Jul. 18, 2025. [Online]. Available: https://www.belfercenter.org/research-analysis/cybersecurity-strategy-scorecard
T. Johansmeyer, G. Mott, and J. R. C. Nurse, “Cyber Strategy in Practice: The Evolution of US, Russian and Ukrainian National Cyber Security Strategies through the Experience of War,” The RUSI Journal, vol. 169, no. 3, pp. 40–51, Apr. 2024, doi: 10.1080/03071847.2024.2377544.
M. Clarke and K. Martin, “Managing cybersecurity risk in healthcare settings,” Healthcare Management Forum, vol. 37, no. 1, pp. 17–20, 2024, doi: 10.1177/08404704231195804.
I. Thornton-Trump, “State of Cybersecurity 2025: Trends, Insights and Strategies for Resilience,” 2025. [Online]. Available: https://whitepapers.theregister.com/paper/view/40177/state-of-cybersecurity-2025-trends-insights-and-strategies-for-resilience
The Institute of Value Management, “Value Management Standards, applying best practice,” The Standard BS EN12973:2020 represents a consensus of views and provides a benchmark of best practice. Accessed: Jul. 20, 2025. [Online]. Available: https://ivm.org.uk/value-management/standards/
M. Law, “EY Study: How Cybersecurity Adds $36m Value per Initiative," Cloud & Cybersecurity. Accessed: Feb. 25, 2026. [Online]. Available: https://technologymagazine.com/articles/ey-study-how-cybersecurity-adds-36m-value-per-initiative
K. Maes, S. De Haes, and W. Van Grembergen, “Developing a Value Management Capability: A Literature Study and Exploratory Case Study,” Information Systems Management, vol. 32, no. 2, pp. 82–104, Apr. 2015, doi: 10.1080/10580530.2015.1018767.
R. H. Ashton, “Value-creation models for value-based management: review, analysis, and research directions,” Advances in management accounting, pp. 1–62, 2007.
G. Barbieri, A. M. Benavides, L. A. Esteves, C. Olaya, and F. Zapata, “Organizational Value Framework for Asset Management Decision-Making,” IFAC-PapersOnLine, vol. 58, no. 8, pp. 395–400, 2024, doi: 10.1016/j.ifacol.2024.08.153.
X. Li, B. Deng, Y. Yin, and Y. Jia, “Critical Obstacles in the Implementation of Value Management of Construction Projects,” Buildings, vol. 12, no. 5, p. 680, May 2022, doi: 10.3390/buildings12050680.
F. Rowe, “What literature review is not: diversity, boundaries and recommendations,” European Journal of Information Systems, vol. 23, no. 3, pp. 241–255, May 2014, doi: 10.1057/ejis.2014.7.
M. Genero Bocco, Métodos de investigación en ingeniería del software. Madrid: RA-MA Editorial, 2014.
B. Kitchenham and S. Charters, “Guidelines for Performing Systematic Literature Reviews in Software Engineering,” UK EBSE-2007-12007, 2007.
W. Mengist, T. Soromessa, and G. Legese, “Method for conducting systematic literature review and meta-analysis for environmental science research,” MethodsX, vol. 7, p. 100777, 2020, doi: 10.1016/j.mex.2019.100777.
G. Lindemulder and M. Kosinski, “¿Qué es la ciberseguridad? | IBM,” ¿Qué es la ciberseguridad? | IBM. Accessed: Jul. 20, 2025. [Online]. Available: https://www.ibm.com/es-es/topics/cybersecurity
F. Schiliro, “Towards a Contemporary Definition of Cybersecurity,” 2023, arXiv. doi: 10.48550/ARXIV.2302.02274.
M. Abomhara and G. M. Køien, “Cyber Security and the Internet of Things: Vulnerabilities, Threats, Intruders and Attacks,” JCSANDM, vol. 4, no. 1, pp. 65–88, May 2015, doi: 10.13052/jcsm2245-1439.414.
DHS, “A Glossary of Common Cybersecurity Terminology,” A Glossary of Common Cybersecurity Terminology. Accessed: Jul. 20, 2025. [Online]. Available: https://niccs.cisa.gov/resources/glossary
ISO/IEC 27032:2023(en), Cybersecurity — Guidelines for Internet security, 2023. Accessed: Apr. 24, 2020. [Online]. Available: https://www.iso.org/obp/ui/es/#iso:std:iso-iec:27005:ed-3:v1:en
A. Dengkeng, A. Halid, G. Pratiwi, A. I. Rachman, S. B, and L. F. Mz, “Cyber Security Challenges and Solutions in Critical Infrastructure: A Systematic Review of Threat Spectrum, Systemic Vulnerabilities, and Multi-Level Protection Strategies,” JLMA, vol. 6, no. 5, pp. 1183–1193, Sep. 2025, doi: 10.37899/journallamultiapp.v6i5.2469.
Y. N. Bravo Delgado and D. F. Zambrano Montenegro, “Seguridad y privacidad en las redes 5g: una revisión sistemática de la literatura: Security and privacy in 5g networks: a systematic literature review,” Rev. Cient. Multi. G-nerando, vol. 5, no. 2, Jul. 2024, doi: 10.60100/rcmg.v5i2.259.
> REPLACE THIS LINE WITH YOUR MANUSCRIPT ID NUMBER (DOUBLE-CLICK HERE TO EDIT) <
Y. Khourdifi, A. El Alami, M. Zaydi, Y. Maleh, and M. Bahaj, “Navigating the cybersecurity maze,” in Agile Security in the Digital Era, 1st ed., Boca Raton: CRC Press, 2024, pp. 1–18. doi: 10.1201/9781003478676-1.
RAE, “valor | Diccionario de la lengua española,” «Diccionario de la lengua española» - Edición del Tricentenario. 2025. Accessed: Mar. 03, 2026. [Online]. Available: https://dle.rae.es/valor
H. C. C. D. Silva, D. S. D. Silveira, J. S. Dornelas, and H. S. Ferreira, “Information Technology Governance in Small and Medium Enterprises - a Systematic Mapping,” JISTEM USP, vol. 17, Dec. 2019, doi: 10.4301/S1807-1775202017001.
A. Levstek, T. Hovelja, and A. Pucihar, “IT Governance Mechanisms and Contingency Factors: Towards an Adaptive IT Governance Model,” Organizacija, vol. 51, no. 4, pp. 286–310, Dec. 2018, doi: 10.2478/orga-2018-0024.
B. H. Díaz Pinzón, J. S. Gómez Medina, J. D. García González, H. A. Melo Román, and F. E. Sanabria Villamizar, “Contribución de las iniciativas de tecnologías de la información en las organizaciones: una revisión de la literatura,” Innovar, vol. 27, no. 66, pp. 41–55, Oct. 2017, doi: 10.15446/innovar.v27n66.66710.
M. Thiry, A framework for value management practice, Second edition. Newtown Square, Pennsylvania: Project Management Institute, Inc, 2013.
E. De Bono, Lateral Thinking: Creativity step by step. New York: Harper & Row, 1973.
Institute Value Management, “Value Management,” IVM. Accessed: Mar. 03, 2026. [Online]. Available: https://ivm.org.uk/value-management/
British Standards Institution, BS EN 1325:2014 Value Management. Vocabulary. Terms and definitions, BS EN 1325:2014, London., 2014. Accessed: Aug. 15, 2025. [Online]. Available: https://knowledge.bsigroup.com/products/value-management-vocabulary-terms-and-definitions
British Standards Institution, BS EN 12973:2020 Value Management, BS EN 12973:2020, London., 2020. Accessed: Sep. 28, 2020. [Online]. Available: https://shop.bsigroup.com/ProductDetail/?pid=000000000030314082
L. Alevizos, L. Bhakuni, and S. Jäschke, “A value driven framework for cybersecurity innovation in transportation and infrastructure,” International Journal of Information Technology, vol. 17, no. 1, pp. 321–331, Jan. 2025, doi: 10.1007/s41870-024-02288-w.
C. Aksoy, “Are critical success factors for cybersecurity just technical issues Cybersecurity management and the human factor,” Pressacademia, p. 2, Jun. 2023, doi: 10.17261/Pressacademia.2023.1735.
I. Jebril, R. Almaslmani, B. A. F. Jarah, M. I. Mugableh, and N. Zaqeeba, “The impact of strategic intelligence and asset management on enhancing competitive advantage: The mediating role of cybersecurity,” 10.5267/j.uscm, vol. 11, no. 3, pp. 1041–1046, 2023, doi: 10.5267/j.uscm.2023.4.018.
F. Kitsios, E. Chatzidimitriou, and M. Kamariotou, “The ISO/IEC 27001 Information Security Management Standard: How to Extract Value from Data in the IT Sector,” Sustainability, vol. 15, no. 7, p. 5828, Mar. 2023, doi: 10.3390/su15075828.
H. M. Melaku, “A Dynamic and Adaptive Cybersecurity Governance Framework,” Journal of Cybersecurity and Privacy, vol. 3, no. 3, pp. 327–350, Jun. 2023, doi: 10.3390/jcp3030017.
W. Okori and S. Buteraba, “Cyber Security Exploits and Management in Telecommunication Companies: The Case of Uganda,” Journal of Computer Science and Technology Studies, vol. 6, no. 4, pp. 67–76, Oct. 2024, doi: 10.32996/jcsts.2024.6.4.10.
M. F. Safitra, M. Lubis, and H. Fakhrurroja, “Counterattacking Cyber Threats: A Framework for the Future of Cybersecurity,” Sustainability, vol. 15, no. 18, p. 13369, Sep. 2023, doi: 10.3390/su151813369.
W. Tan, B. Guo, and Q. Zhang, “Cybersecurity governance and corporate market value: Perspectives from investor trust and supply chain trust,” Pacific-Basin Finance Journal, vol. 90, p. 102646, Apr. 2025, doi: 10.1016/j.pacfin.2024.102646.
W. Yeoh, S. Wang, A. Popovič, and N. H. Chowdhury, “A systematic synthesis of critical success factors for cybersecurity,” Computers & Security, vol. 118, p. 102724, Jul. 2022, doi: 10.1016/j.cose.2022.102724.
W. Yeoh, M. Liu, M. Shore, and F. Jiang, “Zero trust cybersecurity: Critical success factors and A maturity assessment framework,” Computers & Security, vol. 133, p. 103412, Oct. 2023, doi: 10.1016/j.cose.2023.103412.
M. Petticrew and H. Roberts, Systematic Reviews in the Social Sciences: A Practical Guide, 1st ed. Wiley, 2006. doi: 10.1002/9780470754887.
M. J. Page et al., “PRISMA 2020 explanation and elaboration: updated guidance and exemplars for reporting systematic reviews,” BMJ, p. n160, Mar. 2021, doi: 10.1136/bmj.n160.
Z. Rashid, U. Noor, and J. Altmann, “Economic model for evaluating the value creation through information sharing within the cybersecurity information sharing ecosystem,” Future Generation Computer Systems, vol. 124, pp. 436–466, Nov. 2021, doi: 10.1016/j.future.2021.05.033.
J. Hillmann and E. Guenther, “Organizational Resilience: A Valuable Construct for Management Research?,” Int J Management Reviews, vol. 23, no. 1, pp. 7–44, Jan. 2021, doi: 10.1111/ijmr.12239.
C. B. Silaule, L. M. Makhubele, and S. P. Mamorobela, “A model to reduce insider cybersecurity threats in a South African telecommunications company,” SA Journal of Information Management, vol. 24, no. 1, Oct. 2022, doi: 10.4102/sajim.v24i1.1573.
A. Onumo, I. Ullah-Awan, and A. Cullen, “Assessing the Moderating Effect of Security Technologies on Employees Compliance with Cybersecurity Control Procedures,” ACM Transactions on Management Information Systems, vol. 12, no. 2, pp. 1–29, Jun. 2021, doi: 10.1145/3424282.
I. Bongiovanni, D. Goyeneche, E. Tsen, E. C. James, P. Singh, and R. Ko, “Cyber-attackers as a social force: conceptualizing value sabotage in cybersecurity services,” Journal of Service Management, vol. ahead-of-print, no. ahead-of-print, pp. 1–32, Dec. 2025, doi: 10.1108/JOSM-12-2024-0537.
Manuel De Nicola and Christo Delightson David Raja, “Cybersecurity and Blockchain Impacts on Value Creation Process: Empirical Evidences From Non-financial Disclosure,” Journal of Modern Accounting and Auditing, vol. 18, no. 6, Jun. 2022, doi: 10.17265/1548-6583/2022.06.001.
I. Lee, “Cybersecurity: Risk management framework and investment cost analysis,” Business Horizons, vol. 64, no. 5, pp. 659–671, Sep. 2021, doi: 10.1016/j.bushor.2021.02.022.
M. F. Arroyabe, C. F. A. Arranz, I. Fernandez De Arroyabe, and J. C. Fernandez De Arroyabe, “Exploring the economic role of cybersecurity in SMEs: A case study of the UK,” Technology in Society, vol. 78, p. 102670, Sep. 2024, doi: 10.1016/j.techsoc.2024.102670.
A. Creazza, C. Colicchia, S. Spiezia, and F. Dallari, “Who cares? Supply chain managers’ perceptions regarding cyber supply chain risk management in the digital transformation era,” Supply Chain Management: An International Journal, vol. 27, no. 1, pp. 30–53, Jan. 2022, doi: 10.1108/SCM-02-2020-0073.
T. Sawik, “Balancing cybersecurity in a supply chain under direct and indirect cyber risks,” International Journal of Production Research, vol. 60, no. 2, pp. 766–782, Jan. 2022, doi: 10.1080/00207543.2021.1914356.
P. R. J. Trim and Y.-I. Lee, “Combining Sociocultural Intelligence with Artificial Intelligence to Increase Organizational Cyber Security Provision through Enhanced Resilience,” Big Data and Cognitive Computing, vol. 6, no. 4, p. 110, Oct. 2022, doi: 10.3390/bdcc6040110.
T. Bailetti and D. Craigen, “Examining the Relationship between Cybersecurity and Scaling Value for New Companies,” Technology Innovation Management Review, vol. 10, no. 2, pp. 62–69, Feb. 2020, doi: 10.22215/timreview/1329.
P. S. Aithal, “How to Create Business Value Through Technological Innovations Using ICCT Underlying Technologies,” International Journal of Applied Engineering and Management Letters (IJAEML), vol. 7, no. 2, pp. 232–292, Jun. 2023, doi: 10.47992/IJAEML.2581.7000.0184.
M. Lezzi, A. Corallo, M. Lazoi, and A. Nimis, “Measuring cyber resilience in industrial IoT: a systematic literature review,” Management Review Quarterly, 2025, doi: 10.1007/s11301-025-00495-8.
D. Botha-Badenhorst, “Navigating the Intersection of Innovation and Cybersecurity: A Framework,” European Conference on Research Methodology for Business and Management Studies, vol. 22, no. 1, pp. 18–25, Aug. 2023, doi: 10.34190/ecrm.22.1.1490.
M. F. Franco, F. Künzler, J. von der Assen, C. Feng, and B. Stiller, “RCVaR: an Economic Approach to Estimate Cyberattacks Costs using Data from Industry Reports,” 2023, arXiv. doi: 10.48550/ARXIV.2307.11140.
> REPLACE THIS LINE WITH YOUR MANUSCRIPT ID NUMBER (DOUBLE-CLICK HERE TO EDIT) <
G. P. Platunina, T. Y. Salutina, and I. A. Frank, “Risk Management of Data Transmission Within the Framework of the Digital Transformation of the Telecommunications Industry,” in 2024 International Conference on Engineering Management of Communication and Technology (EMCTECH), Vienna, Austria: IEEE, Oct. 2024, pp. 1–5. doi: 10.1109/EMCTECH63049.2024.10741645.
C.-N. Wang, F.-C. Yang, N. T. M. Vo, and V. T. T. Nguyen, “Wireless Communications for Data Security: Efficiency Assessment of Cybersecurity Industry—A Promising Application for UAVs,” Drones, vol. 6, no. 11, p. 363, 2022, doi: 10.3390/drones6110363.
H. I. Kure, S. Islam, and H. Mouratidis, “An integrated cyber security risk management framework and risk predication for the critical infrastructure protection,” Neural Computing and Applications, vol. 34, no. 18, pp. 15241–15271, Sep. 2022, doi: 10.1007/s00521-022-06959-2.
M. Tsiodra, S. Panda, M. Chronopoulos, and E. Panaousis, “Cyber Risk Assessment and Optimization: A Small Business Case Study,” IEEE Access, vol. 11, pp. 44467–44481, 2023, doi: 10.1109/ACCESS.2023.3272670.
D. Kosutic and F. Pigni, “Cybersecurity: investing for competitive outcomes,” Journal of Business Strategy, vol. 43, no. 1, pp. 28–36, Jan. 2022, doi: 10.1108/JBS-06-2020-0116.
K. Kostelić, “Dynamic Awareness and Strategic Adaptation in Cybersecurity: A Game-Theory Approach,” Games, vol. 15, no. 2, p. 13, Apr. 2024, doi: 10.3390/g15020013.
R. F. Ali, P. D. D. Dominic, S. E. A. Ali, M. Rehman, and A. Sohail, “Information Security Behavior and Information Security Policy Compliance: A Systematic Literature Review for Identifying the Transformation Process from Noncompliance to Compliance,” Applied Sciences, vol. 11, no. 8, p. 3383, Apr. 2021, doi: 10.3390/app11083383.
L. A. Gordon, M. P. Loeb, and L. Zhou, “Integrating cost–benefit analysis into the NIST Cybersecurity Framework via the Gordon–Loeb Model,” Journal of Cybersecurity, vol. 6, no. 1, p. tyaa005, Jan. 2020, doi: 10.1093/cybsec/tyaa005.
S. Islam, N. Basheer, S. Papastergiou, M. Ciampi, and S. Silvestri, “Intelligent dynamic cybersecurity risk management framework with explainability and interpretability of AI models for enhancing security and resilience of digital infrastructure,” Journal of Reliable Intelligent Environments, vol. 11, no. 3, p. 12, Sep. 2025, doi: 10.1007/s40860-025-00253-3.
Z. Bederna and T. Szádeczky, “Managing the financial impact of cybersecurity incidents,” Security and Defence Quarterly, vol. 41, no. 1, pp. 15–35, 2023, doi: 10.35467/sdq/159625.
A. A. Ganin et al., “Multicriteria Decision Framework for Cybersecurity Risk Assessment and Management,” Risk Analysis, vol. 40, no. 1, pp. 183–199, Jan. 2020, doi: 10.1111/risa.12891.
M. A. Hajar et al., “The Effect of Value Innovation in the Superior Performance and Sustainable Growth of Telecommunications Sector: Mediation Effect of Customer Satisfaction and Loyalty,” Sustainability, vol. 14, no. 10, p. 6342, May 2022, doi: 10.3390/su14106342.
S. Saeed, S. A. Suayyid, M. S. Al-Ghamdi, H. Al-Muhaisen, and A. M. Almuhaideb, “A Systematic Literature Review on Cyber Threat Intelligence for Organizational Cybersecurity Resilience,” Sensors, vol. 23, no. 16, p. 7273, Aug. 2023, doi: 10.3390/s23167273.
A. Orlando, “Cyber Risk Quantification: Investigating the Role of Cyber Value at Risk,” Risks, vol. 9, no. 10, p. 184, 2021, doi: 10.3390/risks9100184.
Philip Olaseni Shoetan, Olukunle Oladipupo Amoo, Enyinaya Stefano Okafor, and Oluwabukunmi Latifat Olorunfemi, “SYNTHESIZING AI’S IMPACT ON CYBERSECURITY IN TELECOMMUNICATIONS: A CONCEPTUAL FRAMEWORK,” Computer Science & IT Research Journal, vol. 5, no. 3, pp. 594–605, Mar. 2024, doi: 10.51594/csitrj.v5i3.908.
P. Żebrowski, A. Couce‐Vieira, and A. Mancuso, “A Bayesian Framework for the Analysis and Optimal Mitigation of Cyber Threats to Cyber‐Physical Systems,” Risk Analysis, vol. 42, no. 10, pp. 2275–2290, Oct. 2022, doi: 10.1111/risa.13900.
T. Sawik, “A linear model for optimal cybersecurity investment in Industry 4.0 supply chains,” International Journal of Production Research, vol. 60, no. 4, pp. 1368–1385, Feb. 2022, doi: 10.1080/00207543.2020.1856442.
W. J. Triplett, “Addressing Human Factors in Cybersecurity Leadership,” Journal of Cybersecurity and Privacy, vol. 2, no. 3, pp. 573–586, Jul. 2022, doi: 10.3390/jcp2030029.
H. El Amin, A. E. Samhat, M. Chamoun, L. Oueidat, and A. Feghali, “An Integrated Approach to Cyber Risk Management with Cyber Threat Intelligence Framework to Secure Critical Infrastructure,” Journal of Cybersecurity and Privacy, vol. 4, no. 2, pp. 357–381, Jun. 2024, doi: 10.3390/jcp4020018.
I. Krawczyk-Sokołowska and W. Caputa, “Awareness of network security and customer value – The company and customer perspective,” Technological Forecasting and Social Change, vol. 190, p. 122430, May 2023, doi: 10.1016/j.techfore.2023.122430.
M. N. Y. Marican, S. A. Razak, A. Selamat, and S. H. Othman, “Cyber Security Maturity Assessment Framework for Technology Startups: A Systematic Literature Review,” IEEE Access, vol. 11, pp. 5442–5452, 2023, doi: 10.1109/ACCESS.2022.3229766.
A. Fedele and C. Roner, “Dangerous games: A literature review on cybersecurity investments,” Journal of Economic Surveys, vol. 36, no. 1, pp. 157–187, Feb. 2022, doi: 10.1111/joes.12456.
S. Saeed, S. A. Altamimi, N. A. Alkayyal, E. Alshehri, and D. A. Alabbad, “Digital Transformation and Cybersecurity Challenges for Businesses Resilience: Issues and Recommendations,” Sensors, vol. 23, no. 15, p. 6666, Jul. 2023, doi: 10.3390/s23156666.
M. Kianpour, S. J. Kowalski, and H. Øverby, “Systematically Understanding Cybersecurity Economics: A Survey,” Sustainability, vol. 13, no. 24, p. 13677, Dec. 2021, doi: 10.3390/su132413677.
X. Mu and M. F. Antwi-Afari, “The applications of Internet of Things (IoT) in industrial management: a science mapping review,” International Journal of Production Research, vol. 62, no. 5, pp. 1928–1952, Mar. 2024, doi: 10.1080/00207543.2023.2290229.
N.-A. Perifanis and F. Kitsios, “Investigating the Influence of Artificial Intelligence on Business Value in the Digital Era of Strategy: A Literature Review,” Information, vol. 14, no. 2, Feb. 2023, doi: 10.3390/info14020085.
N. S. Sewpersadh, “Disruptive business value models in the digital era,” Journal of Innovation and Entrepreneurship, vol. 12, no. 1, p. 2, Jan. 2023, doi: 10.1186/s13731-022-00252-1.